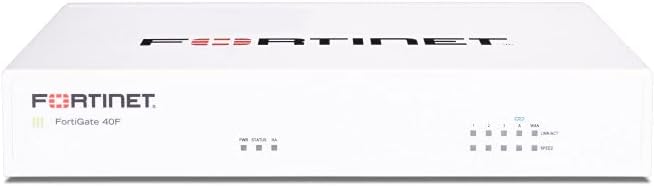
FortiGate-40F
4.2Editor score
Five Gigabit Ethernet ports
Up to one Gbps IPS
Compact fanless desktop design
Our Hardware Firewalls guide compares ten business security appliances for throughput, port options, VPN support, management ease, and feature bundles.
Hardware firewalls give small offices, branch locations, and growing businesses a dedicated layer of network protection without relying on the limited capabilities of a basic consumer router. The right appliance should balance inspection throughput, port flexibility, VPN capacity, threat-prevention features, management tools, and the total cost of owning the equipment and its subscriptions.
We compared ten hardware firewall appliances using the specifications and feature information available for each model. The list covers compact units for small networks, business gateways with software-defined networking features, cloud-managed appliances, and higher-performance models for branch offices or distributed organizations, with special attention to hardware-only limitations.
Each review explains what distinguishes the appliance, who should consider it, and where its trade-offs may matter. Ratings reflect the supplied customer feedback, while missing ratings are represented as zero rather than invented. Retail pricing, bundle contents, licensing options, and availability can change, so confirm the current listing before purchasing.
4.2Editor score

4.7Editor score

5.0Editor score
This side-by-side comparison highlights firewall throughput, physical connectivity, protection features, and management options across ten appliances designed for small businesses, branch offices, and distributed networks.


The FortiGate-40F is a compact next-generation firewall intended for small businesses, enterprise branch offices, and other modest network environments. It carries a 4.2 rating and stands out for delivering capable inspection performance without a large desktop footprint. Five Gigabit Ethernet RJ45 ports, including one WAN connection and four internal ports, make it practical for a basic segmented network.
We may earn a commission when you buy through this link, at no additional cost to you.
Fortinet states that the appliance can provide up to 1 Gbps of IPS throughput and 600 Mbps of threat protection throughput. Its purpose-built security processor is designed to inspect SSL-encrypted traffic, while integration with FortiGuard Labs adds AI-powered threat identification. The management console combines network visibility with automation, and Zero Touch Integration can simplify deployment within a Fortinet Security Fabric environment.
The primary trade-off is clearly identified in the product name: this is an appliance-only offering with no included subscription. That means buyers must independently determine which FortiGuard services, support, and firmware access they need and what they cost over time. The 40F also does not offer the fiber uplinks or multi-gigabit flexibility found in higher-capacity business models.
Despite those limitations, the FortiGate-40F is a compelling choice for a small organization that wants enterprise-oriented firewall architecture in a quiet, space-saving appliance. It is especially suitable for teams that already use or plan to adopt Fortinet products. It is less suitable for buyers expecting a complete threat bundle or high-speed multigigabit networks without purchasing additional services.
The fanless desktop design keeps noise and physical footprint low while providing enough throughput for common small-office connections. Its five-port layout is enough to define separate WAN, server, and user-network segments without requiring a larger chassis.
Management automation, Security Fabric integration, and FortiGuard threat intelligence make the appliance more than a basic router. Buyers should compare subscription requirements carefully because hardware-only protection and subscribed threat services are not interchangeable.
We may earn a commission when you buy through this link, at no additional cost to you.
The Netgate 1100 is a compact security gateway based on pfSense+, combining firewall, router, and VPN functions in a low-power desktop appliance. Its supplied rating is 4.1. It appeals to administrators who value clear software control, a compact enclosure, and a product that can be configured directly rather than managed exclusively through a vendor cloud.
We may earn a commission when you buy through this link, at no additional cost to you.
The dual-core ARM Cortex-A53 processor is specified to deliver near-gigabit routing in common iPerf3 traffic and more than 650 Mbps of firewall throughput. Three switched Gigabit Ethernet ports can be assigned as WAN, LAN, or optional network interfaces. Silent operation and a low power draw make the device suitable for a desk, wall, or small rack where a noisy fan would be inconvenient.
The listing includes pfSense+ software updates for the product's lifetime, Netgate TAC Lite support, and a one-year hardware warranty. Free setup assistance is available from the Technical Assistance Center, which can be valuable to organizations without a dedicated network engineer. The compact size and three-port arrangement, however, may not suit a growing LAN requiring numerous wired devices or redundant connectivity.
The Netgate 1100 is best for a small office, home-based professional operation, lab, or technical user who wants extensive pfSense+ configuration options. It is less appropriate when physical expansion, multigigabit links, or a large number of simultaneous users are central requirements. Adult signature is required for delivery according to the supplied product information.
Preloaded pfSense+ software and lifetime software updates create a straightforward path from unboxing to configuration. The included setup support can also help first-time administrators establish firewall rules, interfaces, and VPN connections.
Low power use and silent operation help the gateway blend into an office. Three configurable Gigabit ports provide enough flexibility for a basic routed network, although they become a constraint as connected devices multiply.
We may earn a commission when you buy through this link, at no additional cost to you.
The Zyxel USGFLEX100H combines a compact fanless appliance with a useful set of small-business security and networking tools. Its 4.0 rating reflects a generally positive buyer response. This model targets growing offices that need more than a basic router but do not require a large enterprise firewall.
We may earn a commission when you buy through this link, at no additional cost to you.
Its hardware includes eight assignable one-gigabit RJ45 ports, 4,000 Mbps of firewall throughput, 1,500 Mbps IPS throughput, and 900 Mbps VPN throughput. Capacity extends to 50 users, 300,000 concurrent sessions, 50 IPsec tunnels, 25 SSL VPN users, and 16 VLANs. WAN load balancing, active-backup failover, link aggregation, and software-defined port assignments provide room for network growth and resilience.
The one-year Entry Defense Pack includes IP, DNS, and URL reputation filtering along with SecuReporter visibility. An optional Gold Security Pack adds anti-malware, sandboxing, web filtering, IPS, and full UTM capabilities. Nebula management supports centralized configuration, policy synchronization, and SD-VPN orchestration, while the interface can remain accessible on the local network after offline firmware updates.
This is a good fit for a small organization seeking VLAN segmentation, VPN access, and cloud oversight without a large appliance. The central caution is licensing: organizations needing full UTM should not mistake the Entry Defense Pack for a complete premium subscription. Buyers should also verify that Tailscale VPN, Secure WiFi access-point support, and other optional capabilities match their required workflow.
Eight software-defined Gigabit ports let administrators assign connectivity as requirements change. Failover, load balancing, link aggregation, and VLAN support add resilience that is often missing from ordinary small-business routers.
Reputation filtering and reporting make the entry bundle useful, while the optional Gold pack broadens protection to malware analysis, sandboxing, IPS, and web filtering. Matching the license tier to the threat controls you actually need is essential.
We may earn a commission when you buy through this link, at no additional cost to you.
The SonicWall TZ280 is a hardware-only next-generation firewall built for small businesses and branch locations. It has the highest supplied rating among the selected appliances at 4.7. Its combination of compact desktop construction, up to 2.5 Gbps firewall inspection, and cloud-oriented deployment makes it a strong middle-tier option.
We may earn a commission when you buy through this link, at no additional cost to you.
Connectivity includes eight one-gigabit Ethernet ports and two one-gigabit SFP ports. Threat-prevention throughput reaches 1 Gbps, while IPsec VPN throughput is listed at 1.2 Gbps. SonicWall's RFDPI inspection engine is central to the appliance's processing design, and SonicOS 8 can provide intrusion prevention, gateway anti-malware, application control, TLS or SSL decryption, multi-engine sandboxing, and reputation-based content and DNS filtering when active service subscriptions are present.
Zero-touch deployment and management through the on-box interface or cloud Network Security Manager support distributed rollouts. Secure SD-WAN, IPsec and SSL VPN, and Zero-Trust Network Access through Cloud Secure Edge broaden its usefulness for branch networks and remote workers. The significant trade-off is that this appliance-only listing explicitly excludes security services, firmware updates, and support.
The TZ280 is a strong recommendation for organizations that want capable branch protection and flexible management but already have a clear SonicWall service strategy. It is less attractive to a first-time buyer who assumes the hardware includes every protection feature. Before deployment, compare the required subscription level with the workload and confirm that firmware updates and support will be obtained promptly.
Up to 2.5 Gbps of firewall inspection is appropriate for higher-speed business connections where full inspection remains practical. Threat-prevention and VPN figures give administrators a more realistic view of expected performance under active security workloads.
Zero-touch provisioning and cloud Network Security Manager options can simplify repeated branch installations. The hardware also supports SFP uplinks, giving administrators more flexibility than a copper-only compact firewall.
We may earn a commission when you buy through this link, at no additional cost to you.
The FortiGate-70G is a next-generation firewall designed for branch offices and small offices that need more physical connectivity than a compact entry model. It carries a perfect supplied rating of 5.0. Ten Gigabit Ethernet RJ45 ports make it particularly attractive for networks with several wired segments, servers, access points, and growth in local devices.
We may earn a commission when you buy through this link, at no additional cost to you.
Integrated capabilities include next-generation firewall controls, intrusion prevention, and web filtering. Secure SD-WAN is designed to improve cloud and SaaS performance while preserving consistent security policy. SSL inspection and application control provide visibility into encrypted traffic and help administrators understand or control the applications traversing the network.
Deployment can be handled through FortiGate Cloud or centralized FortiManager management. Integration with FortiSwitch and FortiAP creates a unified path for secure wired and wireless infrastructure, which is especially useful to organizations already committed to Fortinet. This ecosystem consistency can reduce configuration complexity and simplify ongoing oversight.
The FortiGate-70G is a premium recommendation for branch environments needing numerous Gigabit ports and advanced traffic controls. It may be more than a very small household requires, and administrators should ensure that their staff or service provider can configure SSL inspection, SD-WAN policies, and application controls properly. Its rating and connectivity make it especially attractive for a business that values a unified Fortinet environment.
Ten Gigabit Ethernet connections offer more room than most compact firewalls and make dedicated networks straightforward. The port count is useful when a branch needs separate users, servers, guest access, management, and WAN connectivity.
FortiGate Cloud, FortiManager, FortiSwitch, and FortiAP compatibility support a broader infrastructure strategy. This makes the appliance particularly attractive to organizations that want one security ecosystem rather than isolated products for different network layers.
We may earn a commission when you buy through this link, at no additional cost to you.
The Sophos XGS 128 Gen2 is a hardware-only network security appliance aimed at larger offices that need high-speed local connectivity. No customer rating is supplied for this listing, so the numerical rating is shown as zero rather than suggesting an unverified score. Its primary distinction is a generous set of 2.5-gigabit copper ports combined with a fiber uplink.
We may earn a commission when you buy through this link, at no additional cost to you.
Nine 2.5 GbE ports and one SFP port provide flexible access for modern workstations, access points, servers, and WAN connections. Sophos specifies up to 19.1 Gbps of firewall throughput for larger-office use. SD-WAN optimization supports resilient connectivity and intelligent routing across multiple WAN links, which can improve application performance when business traffic is distributed across different providers.
The VPN-ready architecture supports secure site-to-site networking and encrypted employee access. The device is engineered for visibility, reliable operation, and business network performance, making it more ambitious than a basic small-office gateway. Its design also prepares an organization for future connectivity demands as device speeds and network segmentation requirements increase.
The main limitation is explicit: this is hardware only, and IPS, web security, VPN, and advanced threat defense require a Sophos subscription. It is best suited to an organization that values multigigabit access ports, is prepared to license the relevant security services, and needs more connectivity than a compact appliance can provide. Without a supplied rating, buyers should seek current customer feedback and verify the subscription details before ordering.
Nine copper ports at 2.5 Gbps each offer substantial flexibility for fast switches, workstations, and access points. The SFP port provides an additional route for fiber connectivity without relying exclusively on fixed copper interfaces.
Intelligent routing across multiple WAN connections can help maintain usable application performance during link degradation. This feature makes the XGS 128 relevant to branch networks where continuity matters as much as raw firewall inspection speed.
We may earn a commission when you buy through this link, at no additional cost to you.
The Zyxel USGFLEX700 is a business-class ZyWALL firewall intended for mid-size and larger offices. It has a perfect supplied rating of 5.0 and pairs substantial network capacity with a first year of unified threat management services. The appliance can support up to 500 users, making it more relevant to organizations that have outgrown a small gateway.
We may earn a commission when you buy through this link, at no additional cost to you.
Performance specifications include 5,400 Mbps of SPI firewall throughput, 1,450 Mbps with anti-malware and intrusion detection, and 1,100 Mbps VPN throughput, with up to 1.6 million sessions. Connectivity consists of 12 configurable Gigabit Ethernet ports and two Gigabit SFP fiber ports. These figures support businesses with numerous local devices, multiple network segments, and Internet connections appropriate to the stated recommendation of speeds up to 900 Mbps.
The included one-year UTM bundle covers anti-malware, ransomware blocking, web filtering, application control, and intrusion detection and prevention. Nebula Cloud Pro management adds centralized monitoring and configuration. This combination gives a new buyer useful protection and oversight from the outset rather than requiring every service to be assembled separately from the outset.
This model is a strong fit for a growing office that wants a broad security package, cloud management, and room for several hundred users. The main planning issue is continuity after the included period, since ongoing UTM and management terms should be evaluated before purchase. Buyers should also confirm that their actual application mix and traffic profile align with the stated throughput figures.
Anti-malware, ransomware blocking, web filtering, application control, and intrusion prevention provide multiple layers of protection in the included term. This makes the package particularly approachable for organizations that need a broad security baseline immediately.
A 5,400 Mbps firewall rate, 1.6 million-session capacity, and fourteen physical ports provide room for larger user groups. Copper and fiber interfaces allow the network to evolve without depending on a single cabling approach.
We may earn a commission when you buy through this link, at no additional cost to you.
The SonicWall TZ680 is a high-end small-business firewall with the largest stated firewall inspection capacity in this group. No customer rating is supplied, so its rating is represented as zero. The appliance is intended for distributed organizations and demanding SMB sites that need faster inspection and more flexible high-speed networking than a conventional desktop gateway.
We may earn a commission when you buy through this link, at no additional cost to you.
SonicWall specifies up to 5 Gbps of firewall inspection, 2.5 Gbps of threat prevention, and 2.5 Gbps of IPsec VPN throughput. Connectivity includes eight Gigabit Ethernet ports, two 5G SFP+ ports, and two 10G SFP ports. That mix supports high-speed fiber uplinks and local aggregation while retaining copper access for servers, users, and network equipment.
SonicOS 8 can deliver intrusion prevention, gateway anti-malware, application control, TLS and SSL decryption, Capture ATP multi-engine sandboxing, and reputation-based content and DNS filtering. Secure SD-WAN, IPsec and SSL VPN, and Zero-Trust Network Access through Cloud Secure Edge address distributed-site and remote-worker needs. On-box or cloud Network Security Manager control and zero-touch deployment assist administrators managing multiple locations.
This is a compelling choice for a larger SMB or distributed enterprise that needs high-capacity inspection and premium connectivity. Like the TZ280, it is strictly an appliance-only product, and the listing states that security services, firmware updates, and support are not included. Those requirements must be planned before deployment, and the absence of supplied customer feedback makes independent research especially important.
Two 10G SFP and two 5G SFP+ ports create a strong foundation for fiber-heavy branch networks. They can support modern access switches, uplinks, and WAN services where older Gigabit-only appliances would become a constraint.
SD-WAN, multiple VPN types, and Cloud Secure Edge support make the TZ680 relevant beyond perimeter filtering. It is best evaluated as a branch platform rather than simply as a faster version of a small-office router.
We may earn a commission when you buy through this link, at no additional cost to you.
The FortiGate 60F listing combines Fortinet firewall hardware with 36 months of FortiCare Premium and FortiGuard Unified Threat Protection. Its supplied rating is 4.4. The main advantage is not raw port count but a bundled security and support package intended for medium-sized businesses that want coverage without assembling every service separately.
We may earn a commission when you buy through this link, at no additional cost to you.
Unified Threat Protection includes web filtering and anti-botnet technologies designed to address advanced online threats. FortiCare Premium adds support and service continuity, which can be important for an appliance that sits at the center of a business network. The bundle also reduces the initial complexity of determining which security components should be enabled after installation.
This product is tailored toward organizations needing robust protection without the infrastructure of a large enterprise. It provides a simpler path to a managed security posture, though administrators still need to configure policies, logging, DNS behavior, and user or application access appropriately. A bundled service term does not remove the need for operational planning or regular review.
The FortiGate 60F bundle is a good option for a medium business that values multiyear protection and support alongside the appliance. It may be less suitable for a very small network that only needs basic routing, or for a branch that requires numerous physical ports. Buyers should confirm the hardware's interface count and current physical specifications because the supplied data emphasizes the protection package rather than detailed port capacity.
Combining the appliance with a three-year threat-protection and premium-support package simplifies initial service planning. The bundle also provides a defined support relationship for an important piece of infrastructure.
The product targets organizations that have meaningful security requirements but do not need the scale or complexity of a large data-center appliance. Its appeal lies in a ready security foundation and support access.
We may earn a commission when you buy through this link, at no additional cost to you.
The Cisco ASA5525-X ASA5525-K9 is a renewed Cisco security appliance that provides a dedicated firewall alternative to a standard business router. It carries a 4.3 supplied rating. Its defining physical feature is an eight-port Gigabit Ethernet configuration, giving it more wired connectivity than the most compact units in the comparison.
We may earn a commission when you buy through this link, at no additional cost to you.
The available product information identifies the ASA5525-X firewall edition and confirms eight Gigabit Ethernet connections. Cisco ASA appliances are traditionally associated with security-focused routing, firewalling, VPN, and centralized network controls. In a renewed deployment, buyers should determine the exact software image, feature set, licensing status, and administrative condition of the particular unit.
Because this is a renewed product, its value can appeal to organizations seeking familiar enterprise networking hardware without buying a new appliance. The trade-off is that the supplied listing offers less detail than the newer models in this guide. It would be prudent to review the return terms, warranty coverage, cosmetic condition, and any included or required licensing before committing it to a production network.
The ASA5525-X is best considered by administrators familiar with Cisco ASA or seeking an eight-port dedicated security device for a small or branch network. It is less attractive for buyers who require clearly documented modern threat services, current SD-WAN features, or straightforward support without verifying the renewed unit's status. Despite those uncertainties, its rating and familiar platform make it a noteworthy alternative.
Eight Gigabit Ethernet ports provide more physical options than a three-port compact gateway. That makes the appliance easier to use in segmented networks that need multiple internal connections and a dedicated WAN path.
A renewed appliance can be practical for experienced administrators, but its effective value depends on condition, licensing, firmware, and support. Reviewing the listing details and return coverage is essential before deployment.
We may earn a commission when you buy through this link, at no additional cost to you.
Selecting a hardware firewall requires balancing network capacity, security subscriptions, physical connectivity, management requirements, and expected growth. The most important starting point is the real traffic profile of the network rather than the fastest headline performance number.
Firewall throughput describes how much traffic the appliance can process under specified conditions, while threat-prevention, IPS, and VPN figures reflect more demanding inspection workloads. A useful comparison applies the manufacturer's stated conditions consistently and leaves enough headroom above the organization's busiest internet connection and internal traffic requirements.
Choose throughput based on actual traffic, not maximum potential. For most offices, sustained performance well above the WAN connection is more valuable than a headline figure that only applies to basic packet forwarding.
Count the WAN connections, internal user segments, servers, access points, management interfaces, and any failover links the firewall must support. Also examine port speed, configurable WAN or LAN assignments, link aggregation, and SFP options because a sufficient port count at the wrong speed can still restrict a network.
Prefer extra configurable ports when growth is likely, but do not purchase unused capacity blindly. Confirm that the physical layout fits the intended desk, wall, or rack space and that existing switches and cabling match the appliance.
Some appliances arrive with a year of full unified threat management, some include only an entry security bundle, and others are sold without protection services. Hardware-only listings may also exclude firmware updates or support, so the difference between the appliance and its complete operating environment must be clear.
Create a list of required features such as IPS, anti-malware, web filtering, sandboxing, application control, DNS security, and VPN support. Then price the necessary service terms as part of ownership rather than treating the hardware as the complete solution.
Remote employees, branch-to-branch traffic, contractors, and mobile users can make VPN capacity a deciding factor. Compare the number of supported tunnels or concurrent users, available IPsec and SSL VPN options, and whether additional protocols such as Tailscale are relevant to the organization.
Do not confuse VPN throughput with total firewall throughput. Encryption and inspection create additional processing demands, so choose an appliance that preserves acceptable performance when remote-access traffic is active.
Local management gives administrators direct access and can remain useful during internet outages, while cloud platforms simplify monitoring, policy synchronization, and support for distributed sites. Some appliances support both, allowing centralized oversight with local control when needed.
Consider the size and technical maturity of the IT team. A cloud-managed appliance may be easier to maintain, while a locally managed system can provide greater control for a team experienced with firewall configuration.
A firewall becomes more valuable when its threat intelligence, application signatures, web categorization, and detection engines remain current. Review the vendor's reputation-filtering, sandboxing, machine-learning, botnet, and behavioral capabilities, but also examine whether those features require an active subscription.
Treat feature lists as a starting point rather than a guarantee of prevention. Safe configuration, timely updates, sensible policy design, and regular monitoring remain essential even when the appliance supports advanced threat defense.
Look for VLAN support, SD-WAN, VPN, cloud application visibility, and centralized policy controls when the business is adding locations or moving more workloads to cloud services. These capabilities can make a firewall easier to integrate with switches, access points, and remote sites.
A platform that grows with the business may reduce future migration work. Confirm compatibility with the wider vendor ecosystem, especially if switches, wireless access points, or management systems are already in use.
Check whether technical support, firmware maintenance, zero-touch deployment, configuration backup, and recovery assistance are included or separately licensed. These operational services can be as important as inspection speed because an appliance must remain maintainable after installation.
Renewed or hardware-only units deserve especially careful review. Confirm licensing, return terms, warranty coverage, and the availability of updates before placing a renewed or incomplete package on a production network.
Begin by documenting the existing network, including internet circuits, routers, switches, servers, wireless access points, VPN users, and required VLANs. Install the firewall in a location with ventilation, access to power and cables, and enough clearance around the chassis. Connect the WAN interface to the upstream service and use the remaining ports to define internal networks before moving critical equipment.
Configure a management address, administrator credentials, firmware, time settings, logging, DNS behavior, and automatic backup procedures. Create firewall rules from a default-deny posture, permit only necessary traffic, and document the purpose of every broadly permitted rule. Enable threat services, VPN profiles, and SD-WAN policies only after confirming that the relevant subscriptions and licenses are active.
Operate the appliance as part of an ongoing security process. Review logs, utilization, blocked traffic, VPN activity, and policy changes regularly; test critical workflows after updates; and replace or renew support and security terms before expiration. For units with local or cloud management, restrict administrator access, enable multi-factor authentication where available, and keep recovery credentials secure.
A hardware firewall is a dedicated appliance that filters and inspects network traffic according to security policies. A router primarily directs packets between networks, although many consumer routers also include basic firewall functions. Business-grade hardware firewalls generally provide deeper inspection, VPN support, threat intelligence, centralized management, and more sophisticated policy controls.
A hardware-only appliance can provide core firewall and routing controls, but some protection features may remain inactive without a service subscription. Businesses should identify which threat controls they require and confirm whether firmware updates and support are also excluded. A package that includes an appropriate security term may be simpler for a team without dedicated security staff.
The appliance should comfortably exceed the combined demand of its internet connections and important internal traffic. Full threat inspection, IPS, VPN encryption, and heavy application use can reduce performance compared with basic routing figures. Comparing threat-prevention and VPN throughput is therefore more useful than looking only at maximum firewall throughput.
Cloud management is useful for centralized monitoring, policy synchronization, remote support, and repeated branch deployments. Local management can still be preferable when direct control, offline access, or existing administrator familiarity matters. Several appliances support both approaches, so the decision should reflect the organization's team size and operating model.
Many business firewalls can perform routing and replace a separate router, but the configuration must correctly handle the WAN connection, DNS, DHCP, port forwarding, and any provider-specific requirements. Some firewall administrators retain a separate upstream router for easier troubleshooting or compatibility. Confirm the appliance's supported connection methods before removing existing equipment.
Firewall throughput generally represents performance under a less demanding traffic profile. UTM throughput is measured with multiple security services active, such as anti-malware, web filtering, and intrusion prevention, so it is usually lower. Use the more conservative figure when estimating performance under realistic protected workloads.
A renewed firewall can be practical when the device comes from a recognizable platform and the listing provides clear licensing, warranty, return, and condition details. Buyers should verify the exact hardware revision, installed software, feature licensing, and update availability. Production deployments deserve more scrutiny than temporary laboratory use.
Support should be based on combined users, servers, connected IoT devices, and active VPN sessions rather than employee count alone. The listed user capacities provide useful guidance, but session limits, throughput, enabled security services, and application behavior can become constraints first. Organizations with unusually high connection counts should prioritize a higher-tier model.
The FortiGate-40F is a practical budget-oriented choice for a compact small-office environment, while the SonicWall TZ280 stands out as the Editor's Choice for balanced branch performance, flexible ports, and centralized deployment features. The FortiGate-70G takes the premium position because its ten Gigabit Ethernet ports, integrated controls, and unified Fortinet integration suit larger branch networks.
For most buyers, the right priorities are adequate performance under full inspection, enough physical and logical connectivity, and a service package that matches the organization's threat-management needs. VPN capacity, management style, and ecosystem compatibility can be just as important as headline speed, especially for distributed businesses.
Before purchasing, verify the current listing, port configuration, subscription requirements, support terms, and warranty. Retail pricing and bundle contents can change, and a renewed or hardware-only model requires especially careful confirmation. Use the final configuration details—not just the product name—to determine which firewall will serve the network best.